
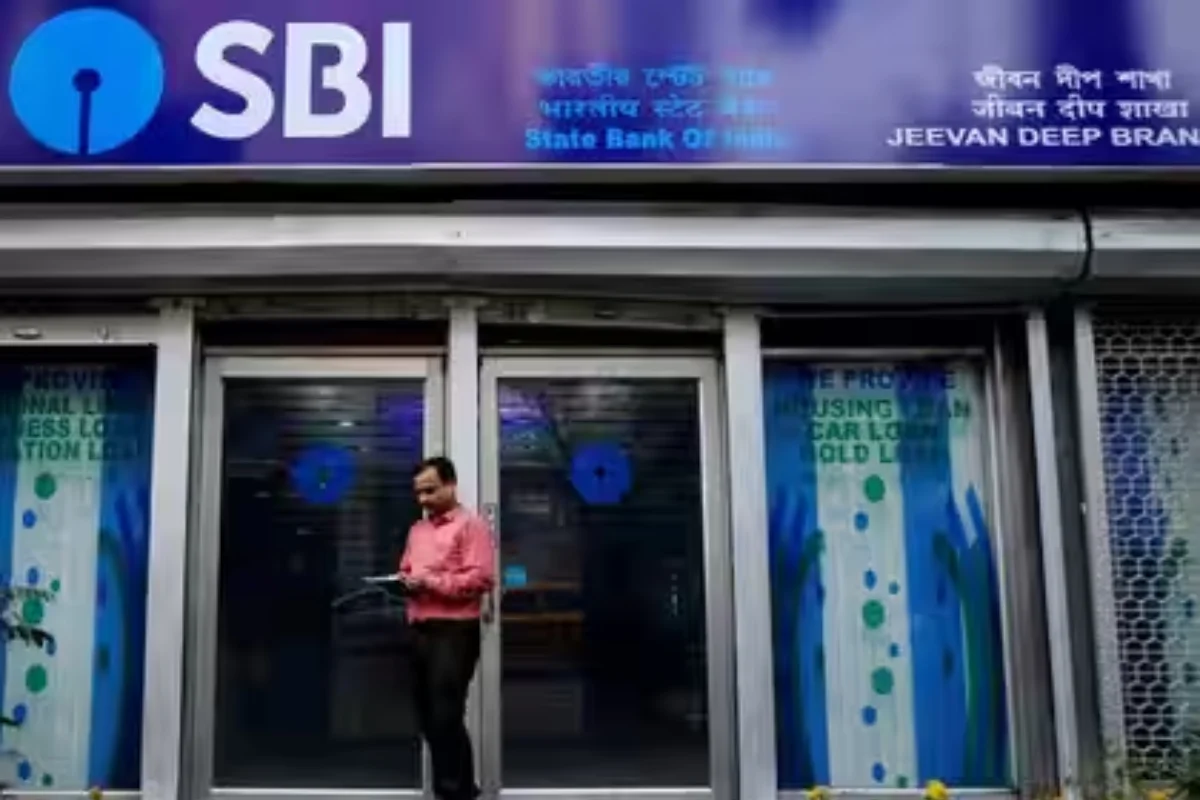
SBI: India’s digital payments and fintech ecosystem handles huge transaction volumes every day, which makes it a rich target. Over the past few years, firms such as Juspay, MobiKwik and Chqbook have faced claims of leaked data on hacker forums, and some companies disputed those claims. Now the country’s largest lender is dealing with a similar scare.
DON'T MISS
What SBI Has Said About the Suspected Leak
SBI said it received alerts on October 16 from its threat intelligence provider, the Defence Cyber Agency and CERT-In. In a first review of roughly 3,75,000 records on the dark web, the bank identified 3,897 with customers’ personally identifiable information. The bank has described the exposure as suspected. It has not confirmed a direct network intrusion, and the figure could change once the investigation ends.
According to the account, a party called Siriusim allegedly held about 3.8 lakh entries in CSV format, along with 2,722 PDF documents linked to SBI.
What Investigators Are Trying to Establish
The inquiry is looking at whether the data is genuine, where it came from, how current it is, and how many customers could be affected. Until then, users should treat the situation as a warning, not a confirmed breach of their own accounts.
How to Protect Your Data
- Never share OTPs, PINs or passwords.
- Turn on transaction alerts
- Change your net banking and UPI passwords
- Avoid unknown links and attachments
- Be careful with callers who quote your details.
- Update your phone and banking apps
What to Do If You Suspect Fraud
Contact your bank immediately and block your card or UPI access if needed. Report cyber fraud on the National Cyber Crime Reporting Portal (cybercrime.gov.in) or by calling 1930. Quick reporting improves the chance of freezing fraudulent transfers.